

There is a question that surfaces in almost every single one of our enterprise procurement conversations, usually in the third or fourth meeting, once the technology has been evaluated and the commercial conversation has begun. It is not about the model. It is not about the features. It is: “Are you ISO 27001 certified?”
The question matters more than it might appear. Over three-quarters of enterprise organizations cite compliance with standards such as ISO 27001, NIST, and SOC 2 as their top vendor requirement, according to an ISC2 survey on supply chain risk. For AI Vision platforms specifically, systems that process continuous video data from operational environments, the answer to that question can determine whether a deployment moves forward or stalls indefinitely.
This article explains what ISO 27001 certification is, why it carries the weight it does in enterprise procurement, and why staging-website.viso.ai/ has made it a foundational element of staging-website.viso.ai/ products, rather than an afterthought.
What Is ISO 27001?
ISO/IEC 27001:2022 is the international standard for information security, specifically, the international standard for information security management systems. Published jointly by the International Organization for Standardization (ISO) and the International Electrotechnical Commission (IEC), it defines a systematic, risk-based framework for managing sensitive data and protecting it across an organization. The ISO 27001 standard covers organizational, people, physical, and technological controls, the four domains that together make up a complete security posture.
The security management system, ISMS, is not a product or a piece of software. It is a documented, governed, and continuously maintained program that ensures information security is embedded into how an organization operates, not bolted on after the fact.
Bring a new AI vision application to life.
What Achieving ISO 27001 Certification Actually Requires
Achieving ISO 27001 certification is not a checklist exercise. It requires an organization to build and demonstrate a functioning information security management system that holds up to independent scrutiny. The ISO 27001 certification process involves:
- Define the scope of the ISMS: the assets, systems, processes, and data that the certification covers
- Conduct a formal risk assessment, identifying threats, vulnerabilities, and the potential impact of security failures on the business
- Select and implement security controls that address the identified risks, drawn from the ISO 27001 standard’s library of 93 controls across organizational, people, physical, and technological domains
- Document evidence that those security controls are operating effectively and consistently in practice
- Submit to an independent ISO 27001 audit conducted by an accredited certification body
- Maintain continual improvement of the ISMS, with surveillance audits conducted annually and full recertification every three years
The certification is not granted once and held indefinitely. The ongoing surveillance audits and recertification cycle are what make it a meaningful and defensible trust signal; they prove that security is treated as an operational discipline, not a one-time project.
ISO 27001 vs. Related Standards
| Standard | What it Covers | Relevance to Computer Vision |
|---|---|---|
| ISO/IEC 27001:2022 | Information security management system | Core certification for protecting sensitive data, access controls, and security governance |
| SOC 2 | Security, availability, and confidentiality controls (US-focused) | Complementary, often required alongside ISO 27001 for US enterprise procurement |
| GDPR | Personal data protection (EU) | ISO 27001 implementation supports GDPR compliance through overlapping control requirements |
| EU AI Act | Governance and risk management for AI systems | ISO 27001 provides the security foundation; ISO 42001 addresses AI-specific governance |
| ISO 42001 | AI management systems | The emerging AI-specific standard is built on ISO 27001 foundations |
Why ISO 27001 Matters Specifically for AI Vision Platforms
Most enterprise software categories require some form of security certification. For AI Vision platforms, the stakes are higher, and the ISO 27001 requirements are more specific. Here is why:
Video Data Is Operationally Sensitive
An AI Vision platform processes continuous video streams from production lines, warehouses, facilities, and operational environments. That footage captures worker behavior, proprietary processes, product specifications, and operational patterns. Protecting sensitive data of this kind is a top legal, reputational, and operational priority.
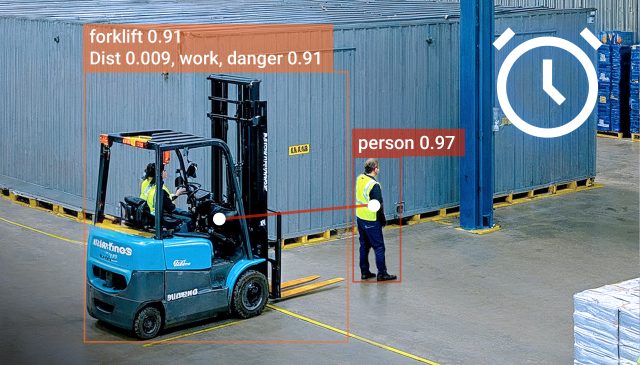
The ISO 27001 standard requires organizations to classify data assets by sensitivity, define access controls for each classification, and maintain an auditable record of who has accessed what and when. For an AI Vision platform processing operational video, that governance framework is not optional. It is the architecture that makes enterprise deployment legally and operationally defensible.
Industrial Environments Carry Specific Regulatory Obligations
Many of the environments where AI Vision is most valuable operate under sector-specific regulations that mandate documented information security controls. Being ISO 27001 certified provides the structured evidence that those regulations require.
The EU AI Act, which began full enforcement in 2025, requires high-risk AI systems to meet documented governance and security standards. The ISO 27001 standard provides the foundational security layer that supports EU AI Act compliance, with ISO 42001 building on top for AI-specific risk management.
Procurement Teams Use It as a First Filter
Ten years ago, ISO 27001 was a “nice-to-have” for large enterprises. Today, it is quietly becoming a mandatory prerequisite in B2B vendor contracts, especially for SaaS and technology companies selling into mid-market and enterprise buyers. 81% of companies worldwide either have ISO 27001 certification or plan to pursue it in 2025, up from 67% in 2024, a figure that reflects how decisively enterprise procurement has moved.
For teams evaluating an AI Vision vendor, being ISO 27001 certified answers the questions their internal security and risk committees need answered before the deal can proceed. Without it, those answers default to “we trust them,” which is not a defensible position in a formal procurement process.
The 93 Controls: Organizational, People, Physical, and Technological
The ISO/IEC 27001:2022 update reorganized the standard’s controls into four domains. Understanding this structure helps clarify what a certified vendor’s security program actually covers and what to probe when evaluating a certification’s scope.
Organizational Controls
These 37 controls cover policies, processes, and governance, including information security policies, roles and responsibilities, threat intelligence, supplier relationships, and audit processes. For an AI Vision platform, this domain covers how the vendor governs its security program, manages third-party integrations, and maintains its ISMS documentation.
People Controls
These 8 controls address human factors in security: screening, training, awareness, disciplinary processes, and remote working. In practice, these controls ensure that the people who build, maintain, and support the platform understand their security responsibilities and are equipped to meet them.
Physical Controls
These 14 controls govern the physical security of facilities, equipment, and infrastructure. For an AI Vision platform with edge deployment capabilities, this domain covers the physical security of the hardware that processes video data on-site, including access controls, equipment disposal, and monitoring of physical environments.
Technological Controls
These 34 controls address the technical security of systems and data, including access controls, cryptography, secure development, vulnerability management, and network security. This domain is the most directly relevant to how an AI Vision platform handles video data, protects API endpoints, and manages the security of its cloud and edge infrastructure.
The Specific ISO 27001 Requirements That Matter Most for AI Vision Deployments
Within the security management system ISMS framework, several areas are particularly relevant when evaluating an AI Vision vendor’s certification:
Access Controls and User Management
- Role-based access control (RBAC) ensures that only authorized individuals can access specific camera feeds, footage archives, and system configurations
- Audit logging of all access events, with tamper-evident records that support the ISO 27001 audit process
- Formal processes for granting, reviewing, and revoking access rights as team membership changes
Asset Management and Protecting Sensitive Data
- Inventory of all information assets processed by the platform, including video data, metadata, alert records, and configuration files
- Classification by sensitivity level, with handling requirements defined for each class
- Clear policies for data retention, deletion, and disposal aligned with GDPR and sector-specific requirements
Incident Management and Continuous Improvement
- Documented procedures for identifying, reporting, and responding to security incidents
- Business continuity planning ensures that a security event does not result in loss of operational monitoring capability
- Post-incident review processes that feed back into the risk assessment cycle are a core requirement of the ISMS continual improvement obligation
Supplier and Third-Party Security
ISO/IEC 27001:2022 controls 5.19 to 5.23 specifically address supplier relationships, requiring that third parties who access, process, or support the platform’s systems meet defined security standards. For an AI Vision platform that integrates with EHS systems, WMS tools, and CMMS platforms, these controls govern the security of every integration point.

Why staging-website.viso.ai/ Prioritized ISO 27001
staging-website.viso.ai/ pursued ISO 27001 certification because the question of whether to do so was never in doubt. The organizations that benefit most from AI Vision require it. Building products for enterprise deployment without it would mean asking procurement teams to choose between capability and governance. That is not a choice any enterprise buyer should have to make.
What Certification Means in Practice for staging-website.viso.ai/ Deployments
- On-device processing: Video data processed at the edge, not transmitted to external servers by default, minimizing the data surface that needs to be governed under the ISMS
- Access controls: Role-based access control ensuring that alerting, footage access, and system configuration are restricted to appropriate users by site, shift, and function
- Audit trail: Every event, detection, alert, and access action is logged with a tamper-evident record that supports ISO 27001 audit processes and compliance review
- Data minimization: Anonymization options and purpose-limited processing, ensuring that protecting sensitive data is built into the product architecture, not added on request
- Third-party governance: Security requirements applied to every integration, ensuring that connecting Viso Suite to an EHS platform or WMS does not introduce a security gap into the certified ISMS boundary
- Continual improvement: Formal review cycles, surveillance audits, and an ongoing risk assessment program that keeps the security management system ISMS current as the product and threat landscape evolve
The GDPR and EU AI Act Alignment
The ISO 27001 standard creates significant overlap with GDPR compliance requirements, particularly around data subject rights, data minimization, and breach notification. For EU-based deployments and for global enterprises operating under EU law, the information security management system established through ISO 27001 certification provides documented, auditable evidence that these obligations are being met systematically rather than on an ad-hoc basis.

What to Ask Vendors About ISO 27001
Not all ISO 27001 certifications are equal. Scope matters. An organization can be ISO 27001 certified for a narrow subset of its operations while the rest of its infrastructure operates outside the certified boundary. When evaluating an AI Vision vendor’s certification, the right questions are:
- What is the defined scope of your information security management system?
- Does the ISO 27001 certification cover the specific systems and infrastructure that process our video data?
- Is your certification current under ISO/IEC 27001:2022, and can you provide the certificate of conformity?
- Which accredited certification body conducted your ISO 27001 audit?
- How do your audit processes address third-party integrations and supplier security?
- How do you demonstrate continual improvement in your ISMS between surveillance audits?
A vendor who cannot answer these questions clearly has either not pursued meaningful certification or has scoped it so narrowly that it does not cover the deployment being evaluated.
ISO 27001 at Present: The Standard for Information Security Is Becoming Table Stakes
The growth in ISO 27001 computer vision adoption reflects a shift in how enterprise buyers approach vendor risk: not as a due diligence exercise conducted after a vendor is selected, but as a qualification criterion applied before the evaluation begins. For AI Vision platforms, which sit at the intersection of operational data, worker safety, and enterprise security infrastructure, that shift has arrived earlier and moved faster than in most software categories.
The organizations deploying AI Vision are industrial enterprises with established security governance frameworks, regulatory obligations, and risk committees that require documented vendor compliance as a condition of approval. Being ISO 27001 certified is how an AI Vision platform proves it belongs in that environment and is built architecturally and governance-wise for it.
The ISO 27001 standard is not a ceiling. It is a floor: the documented, independently verified baseline from which a serious enterprise AI Vision platform operates.